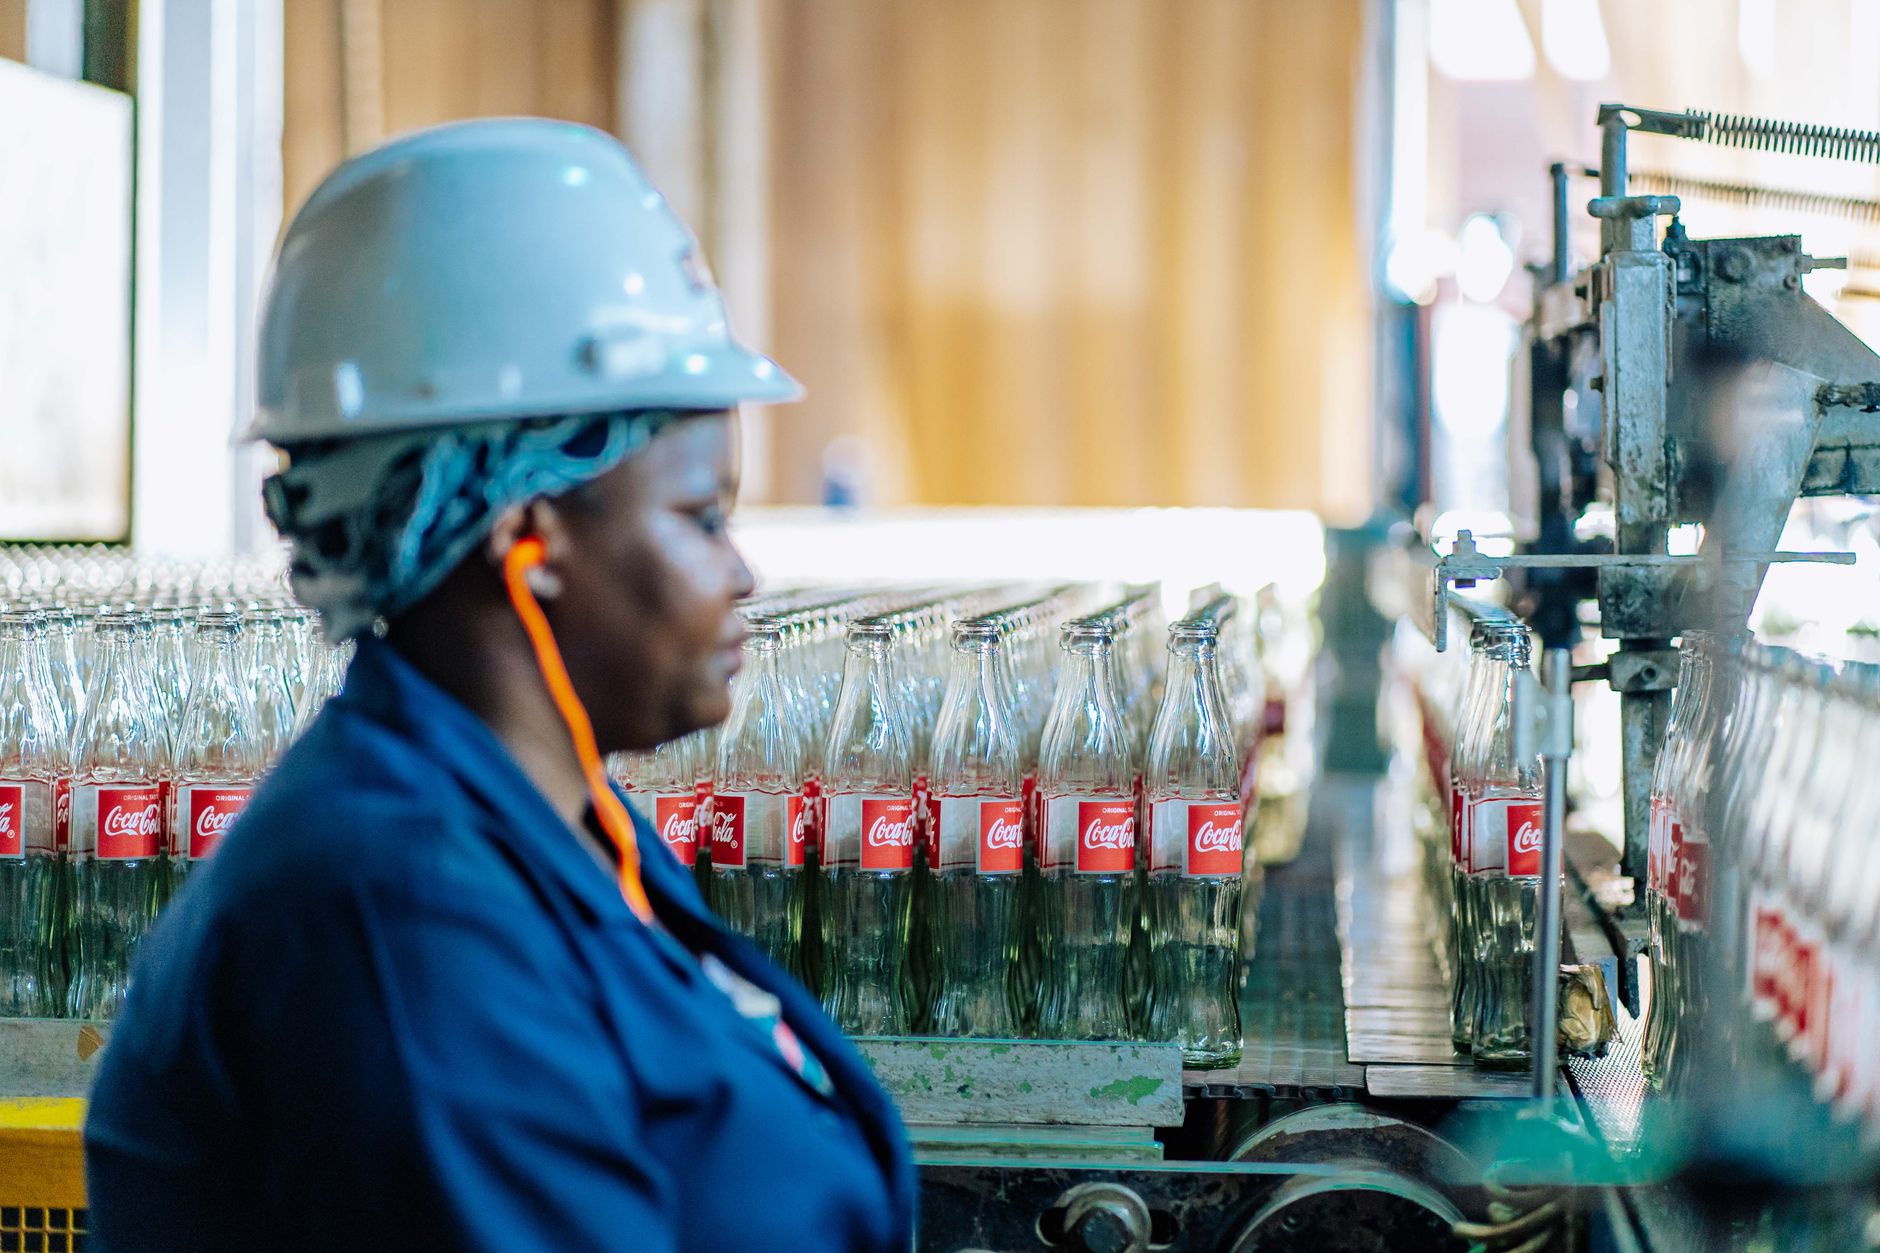
Sharonville food and beverage cybersecurity often breaks at a device that does not look important enough to manage: the maintenance workstation. It may sit beside a packaging line, label printer, scale, refrigeration controller, or quality station. Plant personnel use it occasionally, a vendor may reach it remotely, and nobody is fully certain which team owns its patching, credentials, backups, or replacement plan.
That ambiguity turns one ordinary PC into a bridge between production equipment and the business network. If the workstation can reach email, file shares, an ERP database, programmable controllers, or vendor support tools, a compromise does not remain local. It can interrupt production, corrupt traceability records, or give an attacker a path into systems that were assumed to be separated.
The risk is operational, not theoretical
Food and beverage environments accumulate specialized computers because equipment lasts longer than standard office hardware. A line may depend on a particular driver, USB license key, serial adapter, or unsupported operating system. Replacing the computer can require vendor coordination and production downtime, so teams leave it alone as long as it keeps working.
The result is usually inconsistent control. The office fleet receives centralized patching and endpoint protection, while the plant-floor workstation uses a shared local administrator account. Remote support may be enabled permanently. Antivirus exclusions may be broad because a production application once stopped working. The device may also have open access to shared folders used for labels, recipes, quality documents, or shipping files.
This is where a routine phishing incident or stolen vendor credential becomes a production event. The attacker does not need to understand the machinery. They only need a reachable Windows host with weak identity controls and useful network access.
Build boundaries around function, not location
Putting every device inside the same plant VLAN is not segmentation. A useful design separates business systems, production workstations, industrial equipment, cameras, building controls, guest wireless, and vendor access according to what each system actually needs to communicate with.
The maintenance workstation should reach only the required equipment and services. It should not browse the internet freely, authenticate to unrelated file servers, or connect directly to Microsoft 365 unless there is a documented operational need. Firewall rules should name the specific source, destination, port, and owner. A blanket rule for “the production network” is difficult to audit and even harder to defend during an incident.
This architecture depends on reliable switching, wireless coverage, and cabling. Network separation that exists only in a diagram will fail when an unmanaged switch is added during a rushed line change. A disciplined managed IT services program should keep the physical and logical network maps current as equipment changes.
Vendor access needs an expiration date
Equipment vendors need access, but permanent remote-control software with a shared password is not an access strategy. Each vendor connection should have an identified business owner, an individual account, multifactor authentication where supported, approved hours, and a defined expiration or review date.
For older equipment that cannot support modern identity controls, use a managed jump host or remote-access gateway rather than exposing the production workstation directly. Record who connected, when the session began, and what system was reached. Disable dormant tools and accounts instead of assuming they are harmless.
SentinelOne EDR, Huntress MDR, and SIEM monitoring can provide useful evidence, but plant systems require tuning. A security agent that disrupts a line-control application is not acceptable; neither is excluding an entire directory without review. Effective managed cybersecurity assigns ownership for those exceptions and revisits them when software, vendors, or production workflows change.
Recovery must end with a working line
A successful file restore is not the same as production recovery. The maintenance workstation may depend on local application settings, certificates, drivers, device mappings, license services, and a specific connection to a label or inspection system. If those dependencies are not documented, the restored computer can boot normally while the line remains unusable.
Veeam backup and disaster recovery testing should therefore validate the workflow, not just the backup job. Restore the system in an isolated environment, verify application launch, confirm required network paths, and document the order in which identity, databases, print services, and production interfaces must return. Keep installation media, vendor contacts, license details, and approved configuration records with the recovery plan.
A mature backup and disaster recovery process also accounts for the possibility that credentials were compromised before the outage. Restoring yesterday’s image with the same exposed remote-access account can recreate the incident.
Assign one owner to the boundary
The maintenance workstation usually falls between operations, equipment vendors, and IT. That gap persists until one person or provider owns the inventory, patching decision, security exceptions, vendor access, segmentation rules, and recovery test. The work does not require replacing every legacy system at once. It requires making risk visible and controlling the paths around systems that cannot yet be modernized.
If your Sharonville facility has production workstations or vendor-access tools that no one clearly owns, contact Titan Tech to map the dependencies, close unnecessary network paths, and build a recovery plan that ends with production running.